Microsoft is introducing changes to application permissions as part of its Secure Future Initiative (SFI), which will affect cybersecurity services that use Microsoft 365.
From 31 December 2026, Microsoft will restrict third-party applications, such as CyberSentriq Email Security, from modifying properties like subject, body, or recipients on messages that have already been delivered. Draft messages are unaffected. Applications that need to modify these properties, including for actions like removing malicious links, will require elevated permissions that must be granted by a Microsoft 365 tenant administrator.
Read more here: Upcoming Breaking Changes to Modifying Sensitive Email Properties via Graph API | Microsoft Community Hub
To avoid potential service disruption, affected customers must update their Microsoft 365 permissions in the Platform before 31 December 2026. This must be done by the tenant's Microsoft 365 administrator and cannot be done by an end user.
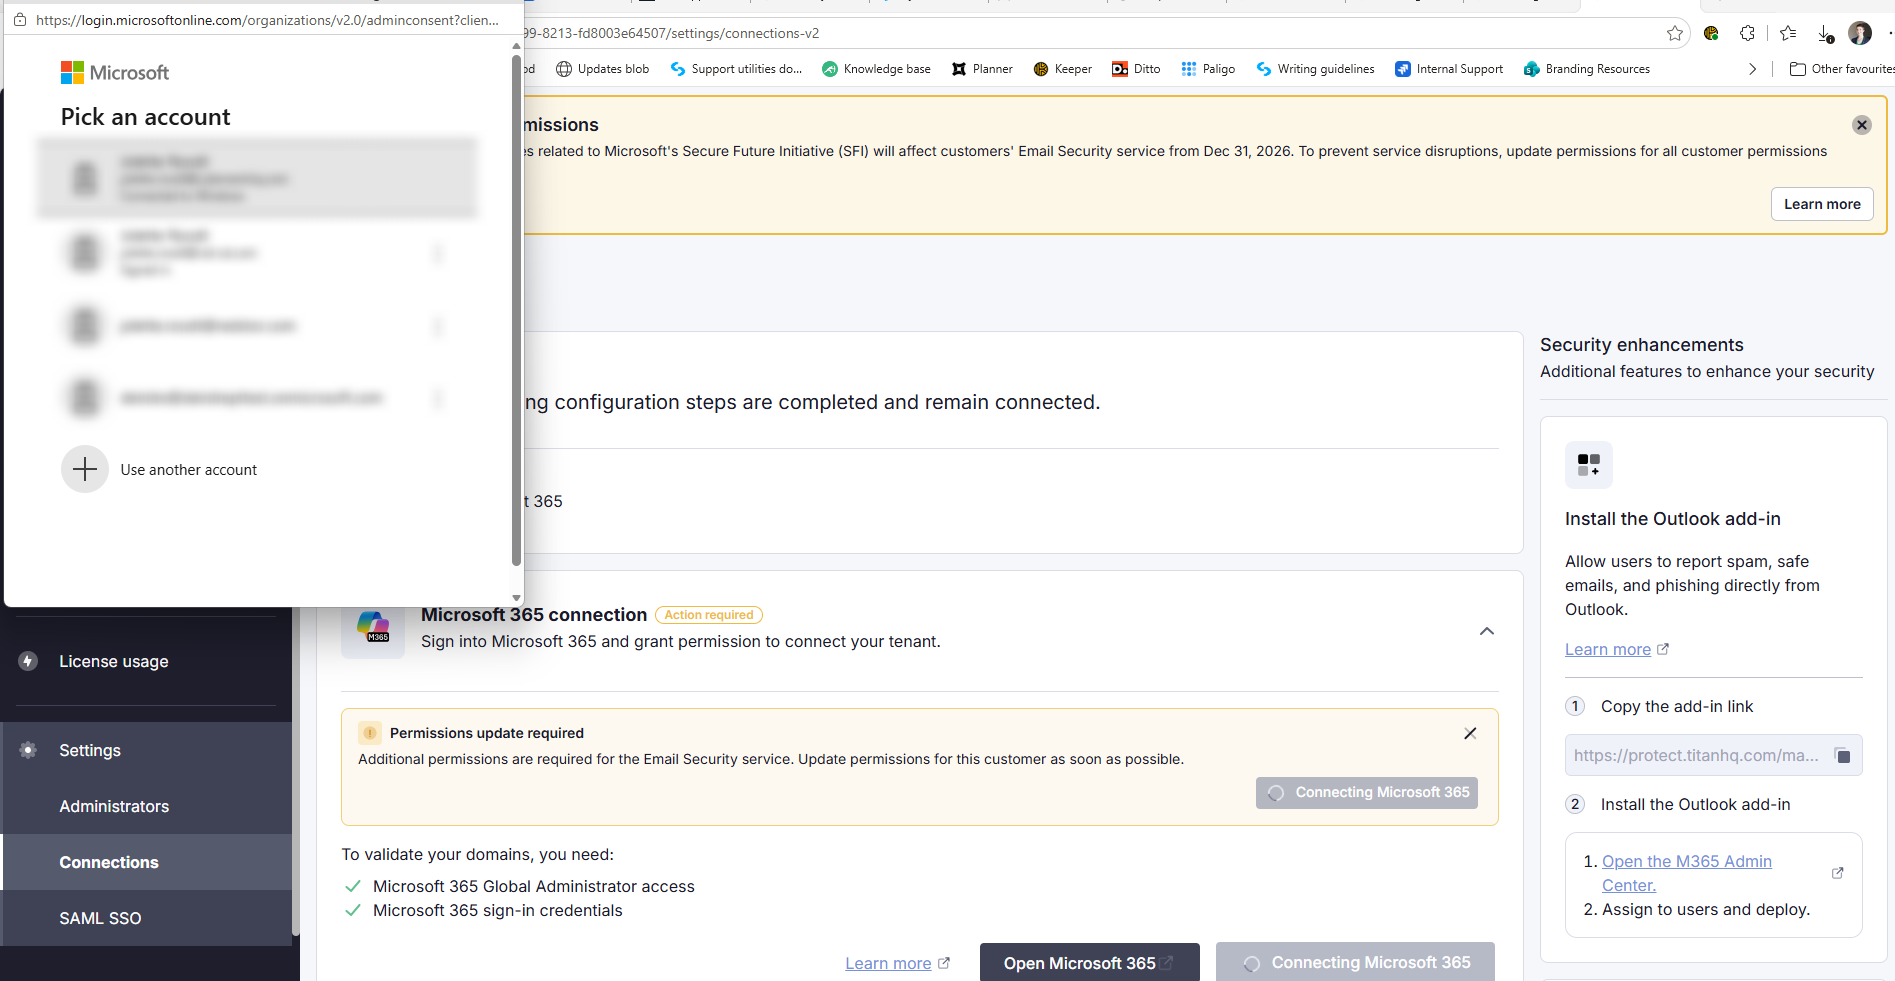
Customers who still need to grant consent to the new permissions are indicated on the Platform with an Update permissions link.
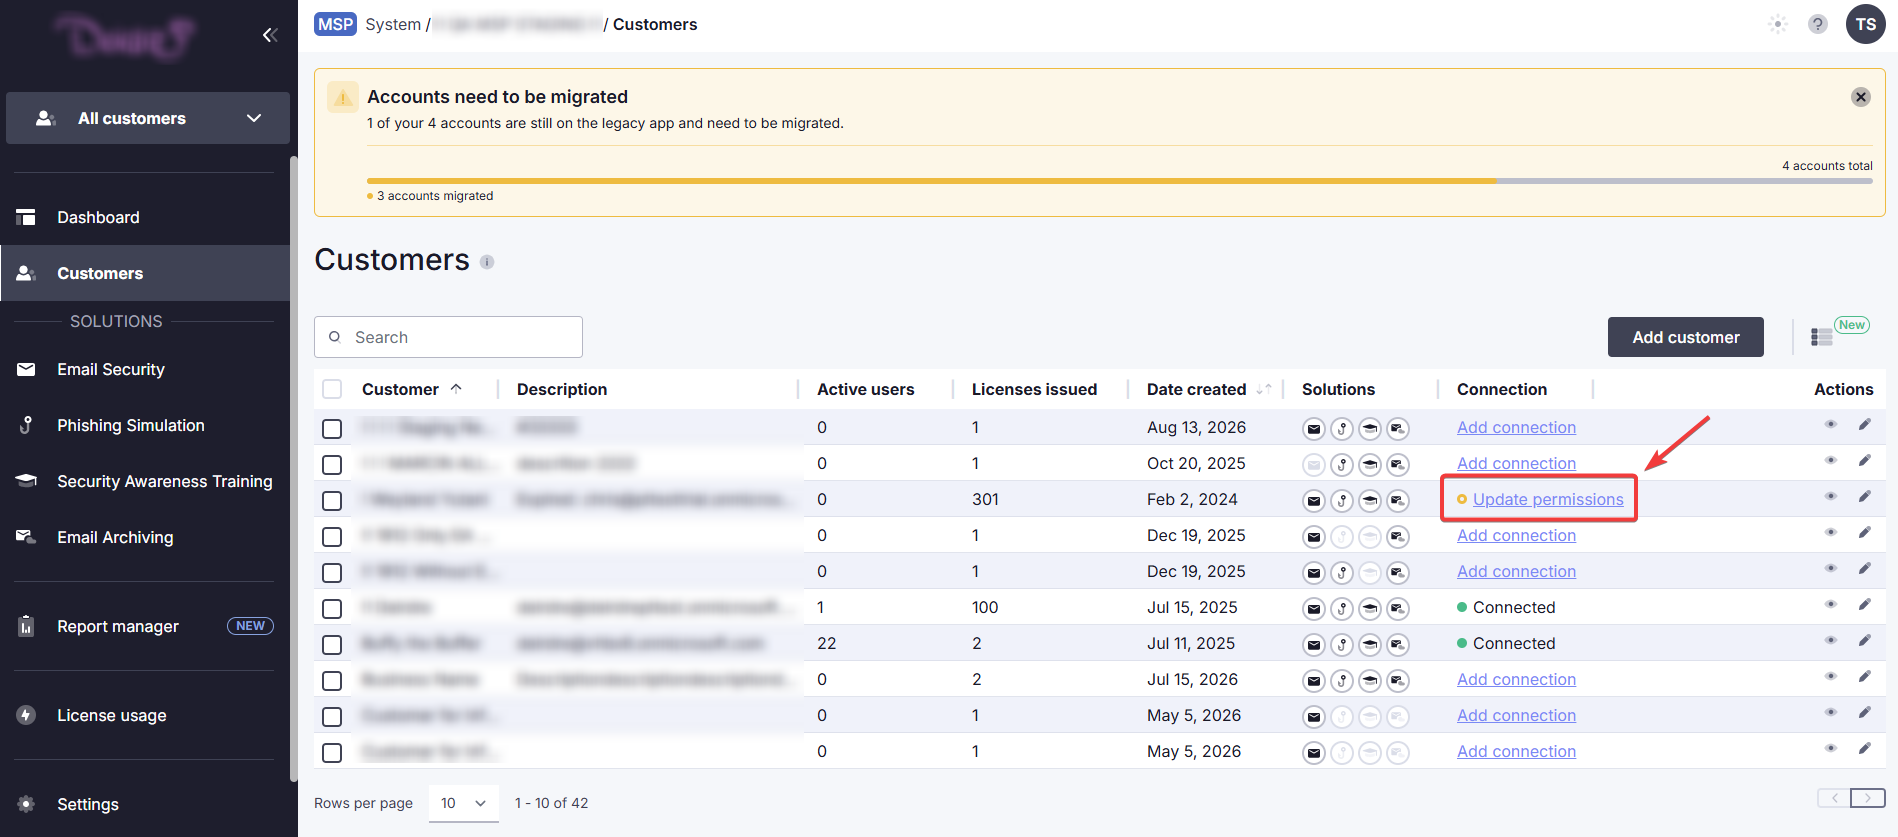
A user with the tenant admin role needs to click on this link, then click on Update permissions at the bottom right.
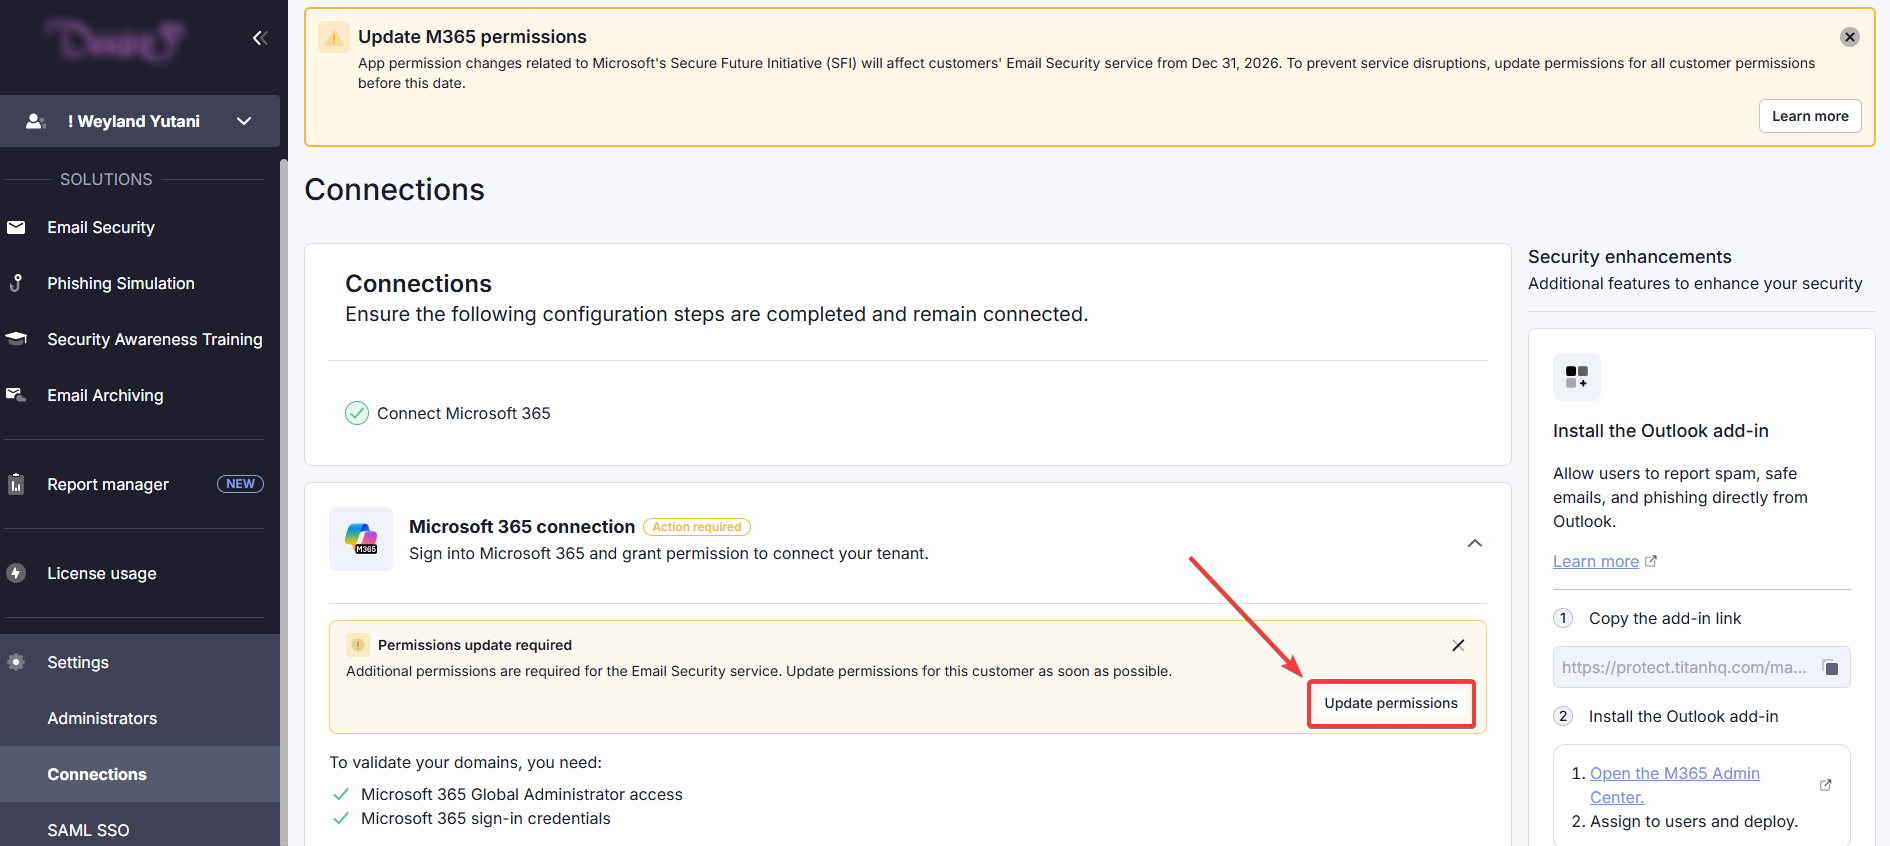
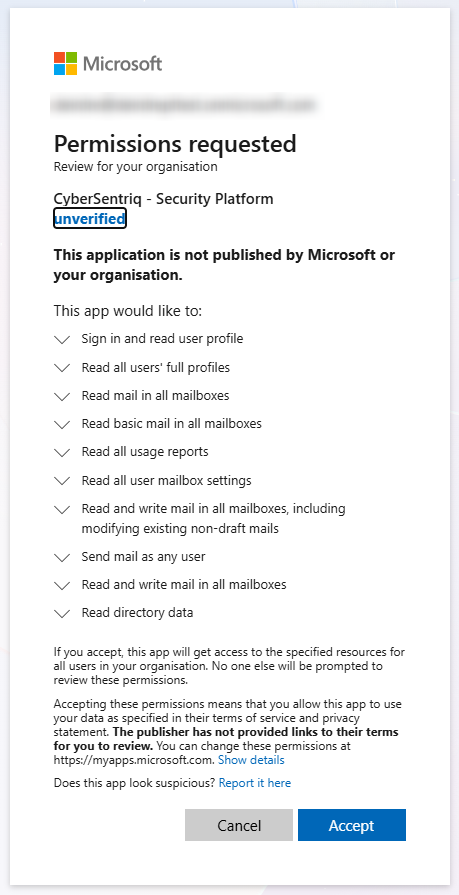
This will open a consent screen where the admin can authenticate with Microsoft 365 and accept the updated permissions.